GRC Consulting Services That Get You Audit-Ready, Faster

We help you meet SOC 2, ISO 27001, HIPAA and GDPR requirements with practical controls, clear policies and a plan your team can actually follow. We map your current gaps, fix them in priority order and get your evidence ready before the auditors arrive.

Challenges

Common Governance,Risk & Compliance Challenges

Navigate complex compliance requirements with practical governance and risk management strategies designed for growth.

Keeping Up with Changing Regulations icon

Keeping Up with Changing Regulations

Compliance requirements such as SOC 2, GDPR, and ISO 27001 continue to evolve. Many organizations struggle to interpret new requirements and implement the necessary controls without disrupting day-to-day operations.

Lack of Documented Policies and Procedures icon

Lack of Documented Policies and Procedures

Many businesses have security practices in place but lack the formal policies, procedures, and evidence that auditors and enterprise customers expect during compliance reviews.

Audit Preparation Takes Too Long icon

Audit Preparation Takes Too Long

Teams frequently scramble before audits to collect documentation, organize evidence, and demonstrate control effectiveness, resulting in unnecessary delays and stress.

Enterprise Deals Stall Due to Compliance Gaps icon

Enterprise Deals Stall Due to Compliance Gaps

Prospective customers increasingly require SOC 2 reports, security questionnaires, or compliance documentation before signing contracts. Missing documentation can slow or prevent sales.

City skyline background for custom AI application call to action

Book A Call

Get Expert Advise

Get Expert Advise
Book a Free Discovery Call
We Offer Governance , risk and compilance

Service

Our GRC Consulting Services

Compliance consulting services that turn frameworks into clear, achievable steps.

Compliance Gap Assessment icon

SOC 2 Compliance Consulting

Get SOC 2 Type I and Type II ready with the right controls and evidence.

SOC 2 Readiness Consulting icon

ISO 27001 Consulting

Build and certify an information security management system.

ISO 27001 Compliance icon

HIPAA Compliance Consulting

Meet HIPAA privacy and security requirements for health data.

GDPR Compliance Support icon

GDPR Compliance Consulting

Handle personal data in line with GDPR and other privacy laws.

Risk Assessment & Management icon

Cybersecurity Risk Assessment Services

Identify, rank and plan fixes for your biggest security risks.

Security Policy Development icon

AI Governance Consulting

Set policies and controls for safe, compliant use of AI in your business.

Process

Our Governance & Compliance Process

A structured approach that transforms compliance into a repeatable business capability.

Assess Your Current Compliance Posture

Phase 1: Assess Your Current Compliance Posture

Timeline: 1-2 weeks

We evaluate your existing security practices, policies, controls, and operational processes against relevant compliance frameworks to identify risks and improvement opportunities.

Deliverables: Compliance Gap Report Risk Register Framework Mapping Improvement Roadmap

  • AI readiness report across data & systems
  • Opportunity map of candidate use cases
  • Current-state architecture overview
  • Stakeholder interview summary
  • Initial risk and compliance flags
Implement Controls & Documentation

Phase 2: Implement Controls & Documentation

Timeline: 2–3

Our consultants help implement technical safeguards, operational controls, and governance documentation required for regulatory and customer compliance.

Deliverables: Security Policies Standard Operating Procedures Implemented Controls Compliance Evidence Library

  • Build-vs-buy recommendation per use case
  • Business case with cost and ROI ranges
  • KPI framework for each initiative
  • Phased roadmap with timelines
  • Prioritized use-case shortlist
Prepare for Audit Success

Phase 3: Prepare for Audit Success

Timeline: 3–4 and ongoing

We organize documentation, validate controls, and prepare your team for external auditors and customer security reviews.

Deliverables: Audit Readiness Checklist Evidence Package Compliance Documentation Security Questionnaire Responses

  • AI governance and decision framework
  • Pilot kickoff plan for the first initiative
  • Quarterly roadmap review structure
  • Handoff brief to delivery teams
  • AI governance checklist

Benefits

What You Gain

Compliance gap assessment icon

Compliance gap assessment

We assess your current practices against frameworks like SOC 2, GDPR, HIPAA, and ISO 27001.

Risk assessment & management icon

Risk assessment & management

We identify and prioritize security and operational risks across your business.

Policy & documentation development icon

Policy & documentation development

We write the security policies and procedures auditors and customers expect to see.

Audit readiness support icon

Audit readiness support

We prepare your team and documentation ahead of formal compliance audits.

Control implementation support icon

Control implementation support

We help implement the technical and process controls required to meet compliance requirements.

Light circuit pattern overlay

Use Cases

Governance, Risk & Compliance Tailored To Your Industry And Business Goals

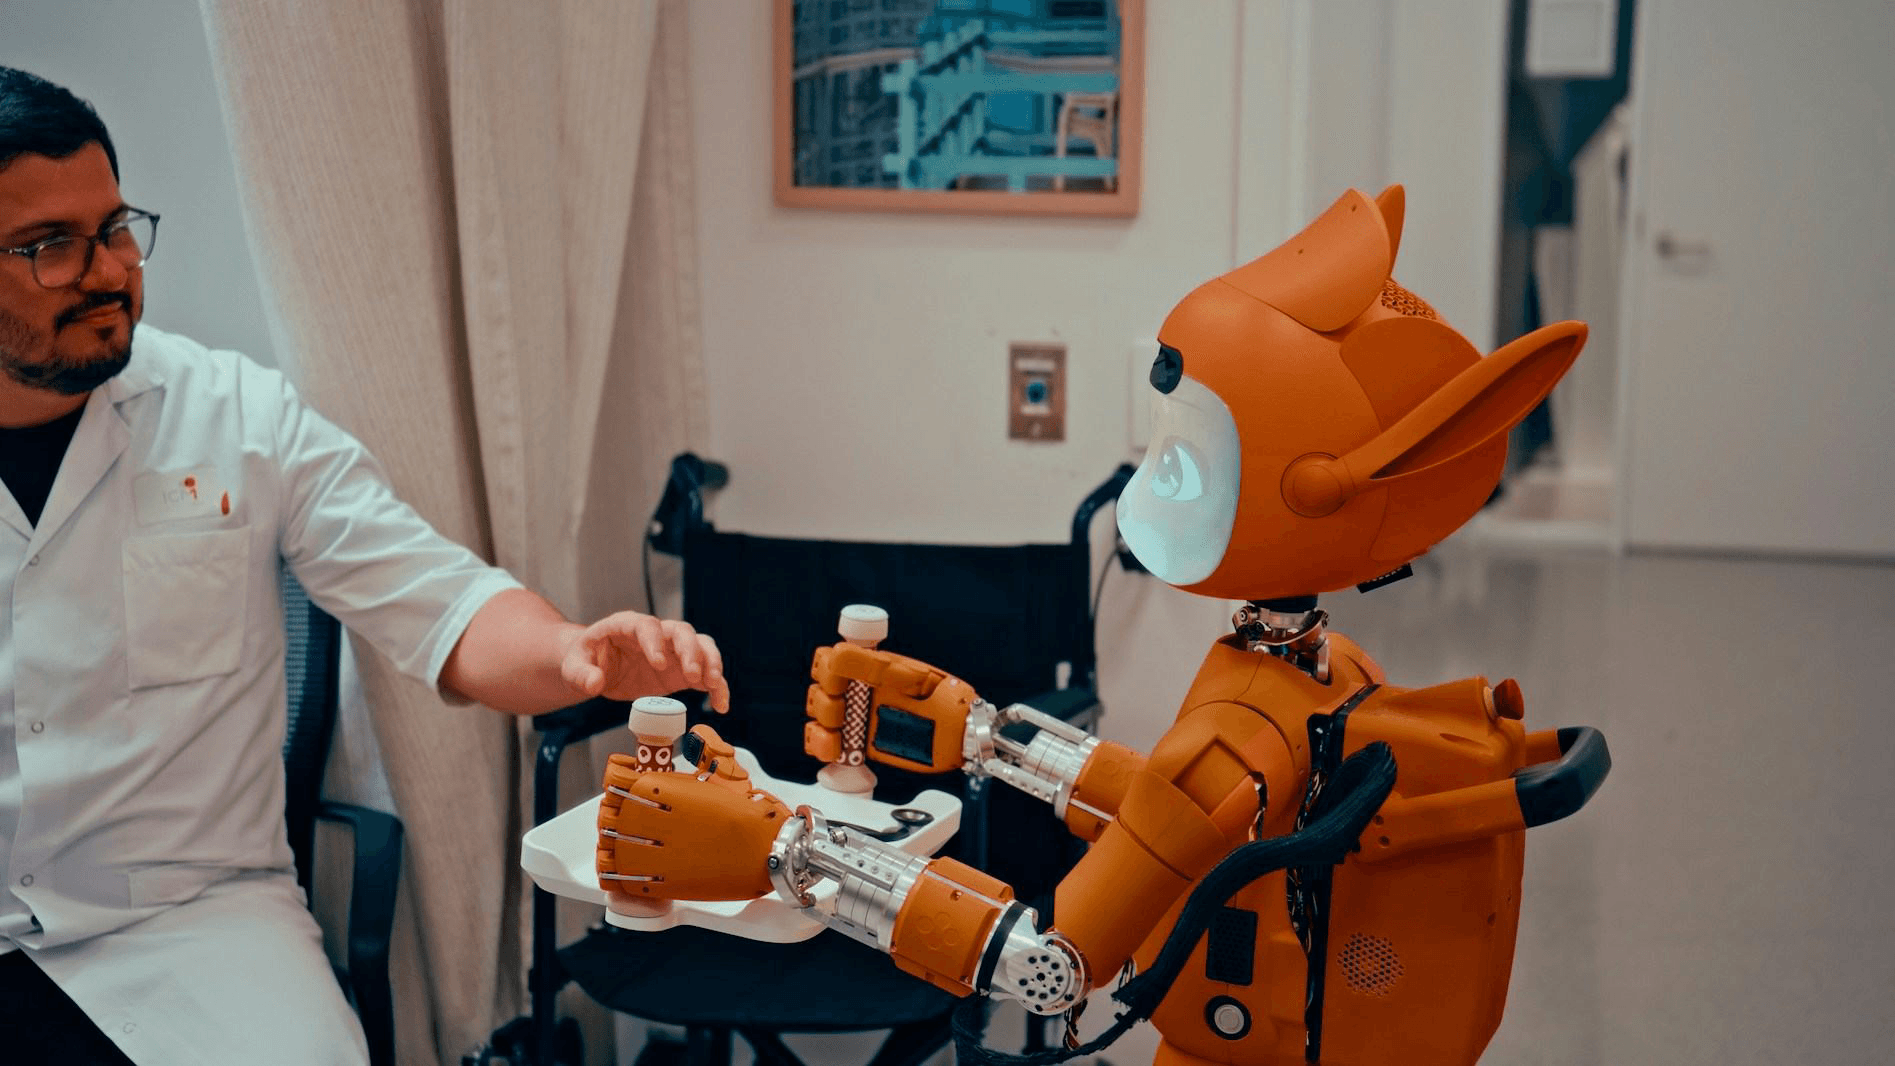
AI-enabled healthcare robotics
healthtech icon

GRC for Healthcare

Healthcare organizations manage highly sensitive patient information while navigating strict regulatory requirements. Novatore Solutions helps HealthTech companies build governance, risk, and compliance (GRC) programs that strengthen security, improve operational resilience, and support patient trust.

  • CheckGovernance for patient-facing applications
  • CheckClinical workflow risk assessments
  • CheckHealthcare security policy development
  • CheckCompliance-ready documentation
Explore Healthcare AI
Subtle circuit pattern

Case Studies

Proven Builds, Not Just Prototypes

Projects Of Novatore Solutions

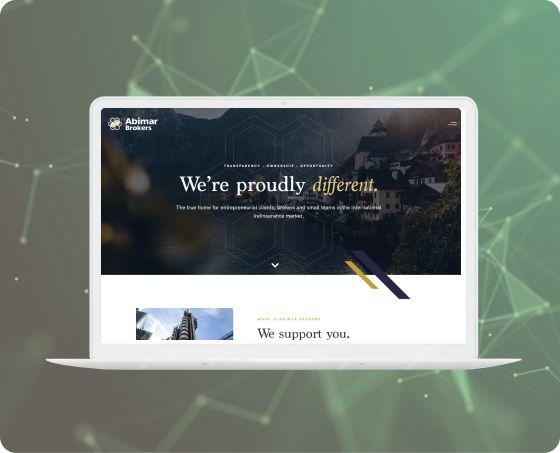
Abimar Brokers
Regulated Industry GovernanceInsurance Compliance

Abimar Brokers

Abimar Brokers is a WordPress-based platform supporting partnership and ownership structures within an internationally focused insurance brokerage. Novatore supported governance-aware practices appropriate for a regulated brokerage environment.

OUTCOME

Governance-aware data handling practices appropriate for a multi-jurisdiction, regulated brokerage environment.

Open case study

Challenge: As an internationally focused insurance brokerage, Abimar needed data handling practices that could stand up to regulatory scrutiny across multiple partnership and ownership structures.

Solution: Novatore applied a governance-aware approach to the platform's data practices, appropriate to the documented process and regulatory expectations of the insurance brokerage industry.

Result: The brokerage operates with data handling practices suited to an internationally regulated insurance context.

Read Case StudyOpen case study details
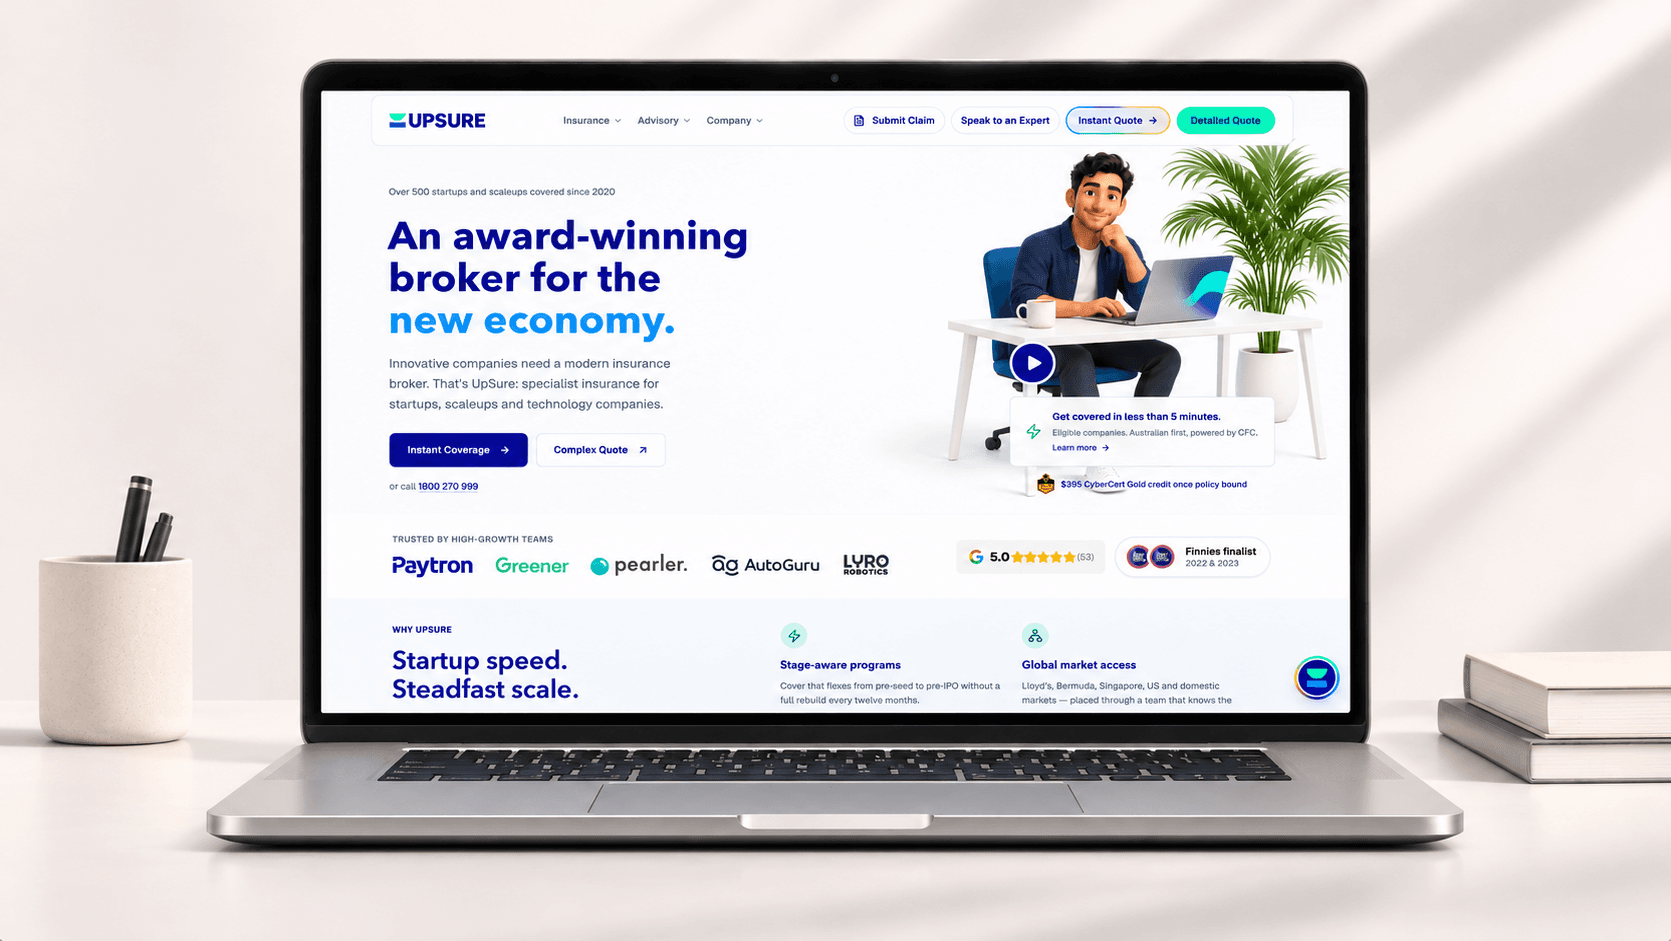
UpSure
AI Agents Fraud Detection

UpSure

A business insurance portal built on React, designed for startups and growth-stage companies to get insured and manage their insurance needs in one place. The platform centralizes insurance documentation, contracts, and renewals that would otherwise be scattered across email threads and paperwork, giving growing businesses a single system to track their coverage.

Renewal Processing Time

40–50% faster

Open case study

Challenge: The platform required stronger governance, secure document management, compliance documentation, and improved operational risk management.

Solution: We conducted compliance assessments, implemented governance controls, developed security policies, and established audit-ready documentation and ongoing compliance processes.

Result: The platform achieved improved governance, stronger security controls, organized compliance documentation, and streamlined compliance management.

Read Case StudyOpen case study details
Subtle circuit pattern

Tools & Technologies

Technologies We Build With

We use proven, production-grade tools and choose the right ones for each project based on performance, cost and security.

OpenAI logo
Claude logo
Meta logo
Gemini logo
Mistral AI logo

FAQs

GRC Consulting FAQs

What teams usually ask before starting a compliance project.

GRC is how a company sets its security policies, manages risk and proves it meets standards such as SOC 2, ISO 27001, HIPAA and GDPR. A GRC program maps your current gaps, fixes them in priority order and keeps the evidence that auditors and enterprise customers ask for.

It depends on your industry and customers; SOC 2 is common for B2B SaaS, while HIPAA and GDPR apply based on the data you handle. We help identify the right framework during the gap assessment.

Most businesses need two to four months to implement controls and documentation before a Type I audit, depending on current maturity.

No, formal audits are performed by accredited third-party auditors; we prepare your controls, documentation, and evidence so the audit goes smoothly.

No, many startups pursue SOC 2 or GDPR readiness early because enterprise customers require it before signing a contract.

Yes. We help organizations prepare for ISO 27001 by assessing existing controls, developing required policies, implementing security practices, and preparing documentation for certification readiness.

Most compliance frameworks require security policies, risk assessments, incident response plans, access control procedures, vendor management documentation, and evidence that controls are operating effectively. We help create and organize these documents.

Compliance is an ongoing process. We provide continuous support through periodic risk assessments, policy updates, control reviews, and audit preparation to help your organization maintain compliance as your business grows.

Light circuit pattern overlay

Your Go To Business Partner

Why Novatore

An AI-Native technology partner icon

An AI-Native technology partner

We combine strategy and delivery to build what actually ships, from roadmap to production

Teams Which Deliver icon

Teams Which Deliver

Strategists, engineers, and QA specialists work as one team to turn plans into software fast.

Full-stack technical depth icon

Full-stack technical depth

React, Next.js, Node.js, Flutter, and Laravel expertise, paired with modern AI and cloud tooling, covers the full delivery lifecycle.

US, UK, and Canadian Clients icon

US, UK, and Canadian Clients

We work inside the timelines, communication norms, and compliance expectations our North American and UK clients require.

Backed by 50+ shipped platforms icon

Backed by 50+ shipped platforms

50+ products delivered from concept to production across HealthTech, FinTech, retail, and SaaS, with proven experience

AI processor technology background

Ready to know where AI actually pays off for you?

Ready to talk about Governance, Risk & Compliance?

Book a discovery call with Novatore Solutions and let's map the right approach for your business.

CONTACT US

Let's Turn Ideas Into Impact.

Have a challenge worth solving or an idea worth building? Let's explore it, shape it, and turn it into a solution that creates real impact.

info@novatoresols.com+1 (206) 738-2549

8 The Green STE B Dover, DE 19901

Follow Us On_

+1

We typically respond within 1 business day.

By providing a telephone number and submitting this form, you consent to be contacted by SMS text message. Message and data rates may apply. Message frequency may vary. Privacy Policy. Reply HELP for more information. You can reply STOP to opt out of further messaging.