


Hidden Threats Go Undetected
Rule-based monitoring misses subtle attack patterns. AI threat detection spots unusual behavior that rules were never written for.
Our AI threat detection services combine machine learning with expert analysts to monitor your cloud, applications and devices around the clock. You get managed detection and response (MDR) with clear alerts, fewer false positives and plain-language monthly reports. It suits growing companies that need a security operations team without hiring one.
AI Threat Detection Challenges
Why traditional security monitoring misses modern threats, and how AI-powered detection closes the gap.
Rule-based monitoring misses subtle attack patterns. AI threat detection spots unusual behavior that rules were never written for.

Security teams face thousands of alerts a day. Managed detection and response cuts the noise to the threats that matter.
Attackers change tactics constantly, so static rules fall behind. Machine learning adapts as new patterns appear.

Activity across apps, cloud and devices is hard to connect. 24/7 security monitoring brings it into one view.
Book A Call
AI Threat Detection Services
AI-powered cybersecurity solutions, from AI threat detection to cyber threat monitoring services that scale with your business.
Managed detection and response (MDR) services: our analysts investigate alerts and contain real threats, so your team doesn't have to.

24/7 security monitoring of your cloud, network, endpoints and applications, with experts ready to respond.
SOC as a service: a full security operations center without building one in-house.
AI threat detection that uses machine learning to spot unusual behavior and new threats that rules miss.
MDR services for small business: enterprise-grade threat detection sized and priced for smaller teams.

Incident response services for fast investigation, containment and recovery when a security incident happens.
AI Threat Detection Process
Our AI threat detection process builds a baseline of normal activity, trains detection models on it and tunes them on real alerts.

Timeline: 1-2 weeks
We analyze your historical logs and activity to build a baseline of normal behavior across your systems.
Deliverables:

Timeline: 3–6 weeks
We build and test AI threat detection models against past incidents and known attack patterns.
Deliverables:

Timeline: Report & Remediate
We connect detection to your monitoring stack and tune it on real alerts, so it gets more accurate over time.
Deliverables:
AI Threat Detection Benefits
AI-powered monitoring spots unusual activity in real time.

Smarter detection filters out noise, so analysts focus on real threats.
Detect account takeovers and evolving fraud patterns early.

Actionable alerts go straight to the right people with context.
AI threat detection models improve with every incident they see.
AI Threat Detection Use Cases
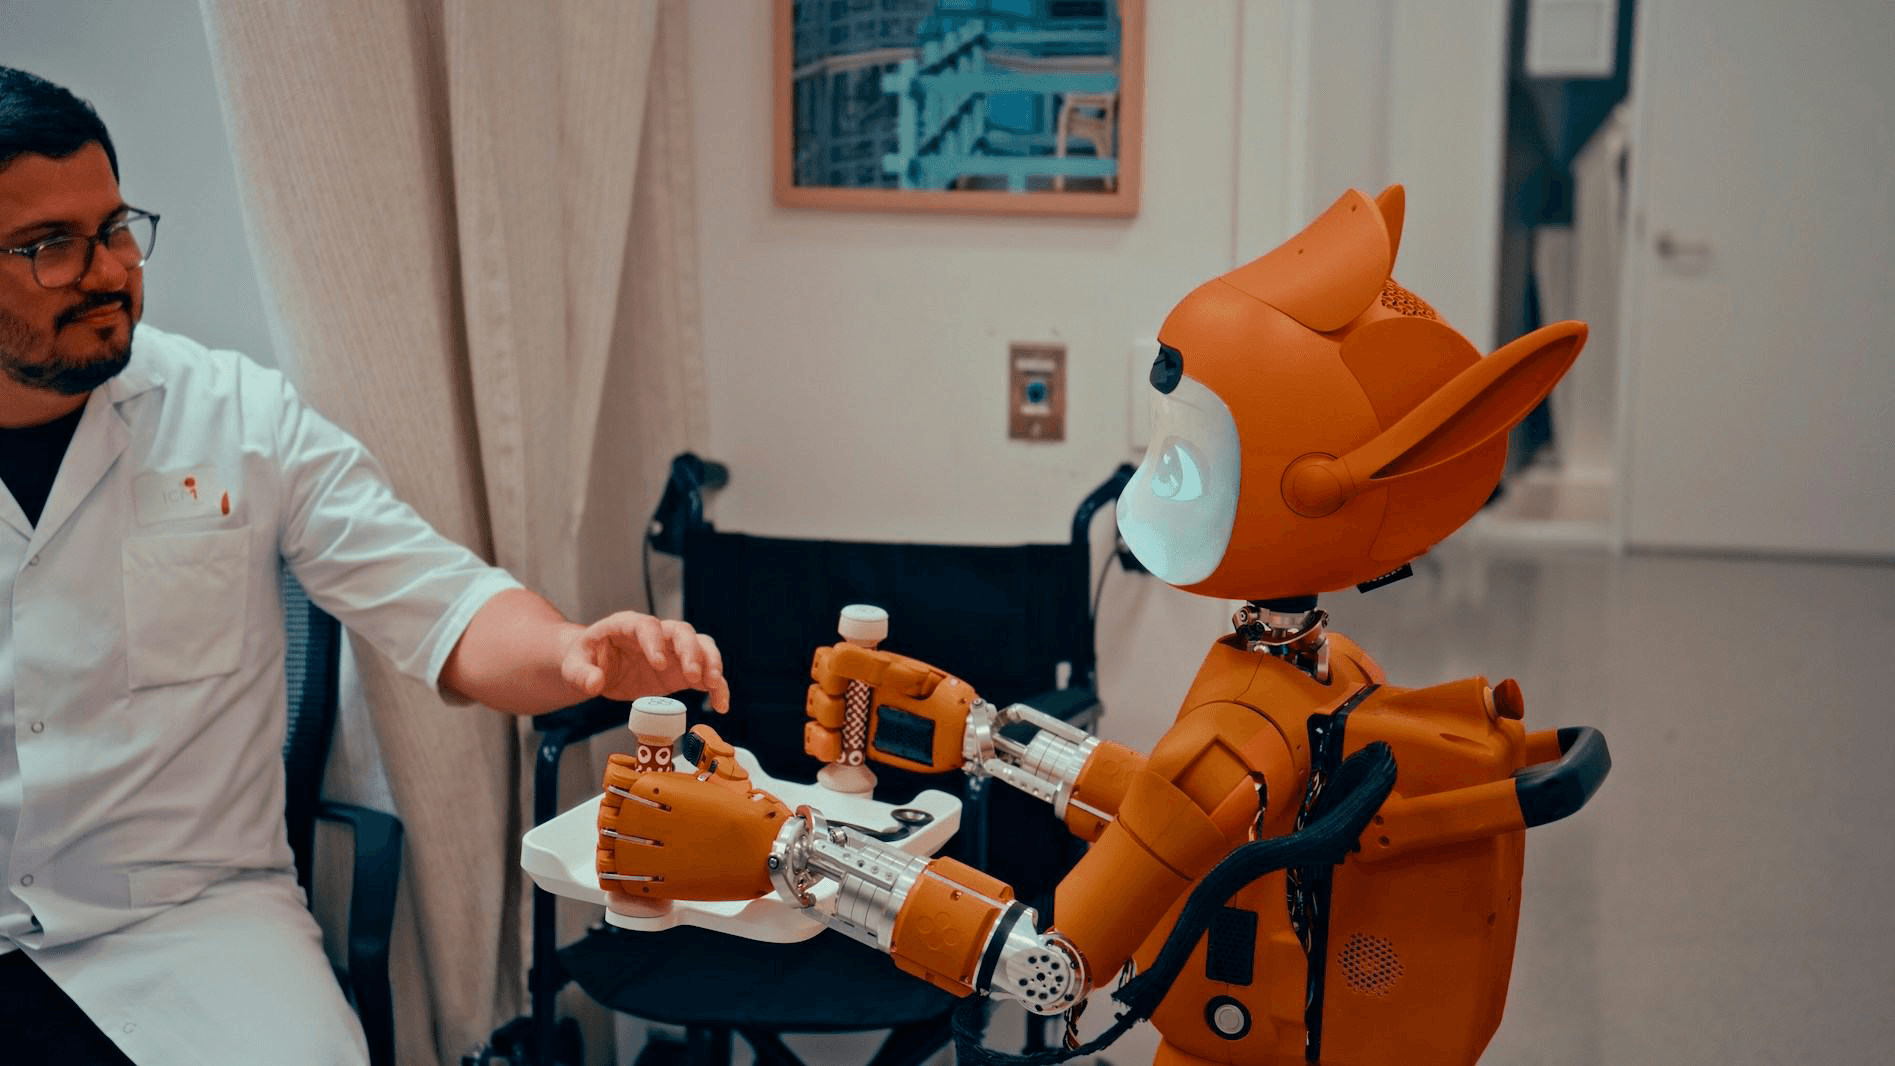

AI threat detection for healthcare: protect patient-facing applications and health data with 24/7 monitoring.
 AI threat detection for EHR, patient portals and medical devices.24/7 monitoring of access to protected health information.Detect ransomware activity early, before it spreads.Incident reports that support HIPAA breach obligations.
AI Threat Detection Tech Stack
We use proven, production-grade tools and choose the right ones for each project based on performance, cost and security.


AI Threat Detection FAQs
Answers to common questions about ai threat detection services, including cost, timelines and how we work.
AI-augmented threat detection uses machine learning to monitor activity across your cloud, applications and devices around the clock. It flags behavior that looks like an attack. Security analysts review and respond to the alerts, so threats are caught earlier, with fewer false alarms than rule-based monitoring alone.
No, it augments it. We layer AI-driven detection on top of standard security monitoring, logging, and access controls, not in place of them.
More data improves accuracy, but we can start with a baseline detection setup even with limited history and refine it as more activity is observed.
We tune detection thresholds against real incident data and continue refining based on analyst feedback after deployment.
Yes, we typically integrate detection models with your existing SIEM or alerting tools rather than building a separate standalone system.
AI-driven monitoring can analyze activity continuously. It can raise alerts in near real time when behavior departs from expected patterns, helping teams investigate threats before they escalate.
No. AI supports security teams by analyzing activity, identifying anomalies, and prioritizing alerts. Human experts remain responsible for investigating findings, validating threats, and deciding how to respond.
AI-powered detection can help identify unusual user behavior, account abuse, fraud patterns, suspicious network activity, insider threats, and automated bot activity across applications and infrastructure
Novatore's rates are $25 to $49 per hour. Managed detection and response is usually priced as a monthly plan based on the number of systems and log sources we monitor.
Why Novatore for AI Threat Detection
We combine strategy and delivery to build what actually ships, from roadmap to production

Strategists, engineers, and QA specialists work as one team to turn plans into software fast.

React, Next.js, Node.js, Flutter, and Laravel expertise, paired with modern AI and cloud tooling, covers the full delivery lifecycle.

We work inside the timelines, communication norms, and compliance expectations our North American and UK clients require.
50+ products delivered from concept to production across HealthTech, FinTech, retail, and SaaS, with proven experience
We are Just One Click Away
Book a free 30-minute discovery call. We'll review your goals, answer your ai threat detection questions and suggest a clear next step, with no obligation.
CONTACT US
Have a challenge worth solving or an idea worth building? Let's explore it, shape it, and turn it into a solution that creates real impact.
