
Hidden Threats Go Undetected
Traditional monitoring often misses subtle attack patterns and unusual user behavior, allowing threats to remain unnoticed until significant damage occurs.
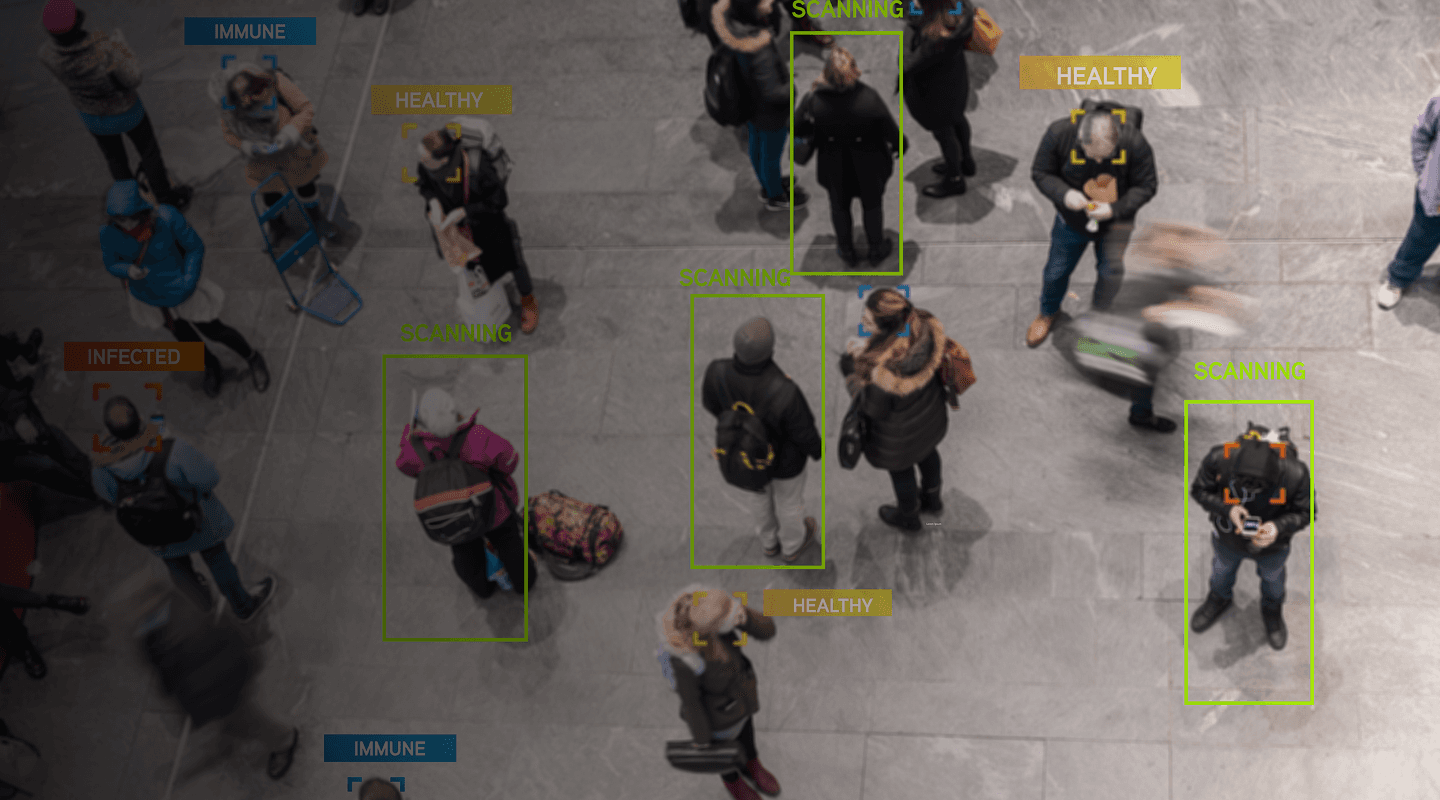
AI Augmented Threat Detection
Novatore Solutions builds threat detection systems that use machine learning to spot unusual activity across applications and infrastructure faster than manual monitoring alone. We combine traditional security monitoring with AI-driven anomaly detection to reduce the time between a threat appearing and being caught.
Challenges
Traditional security monitoring can't keep up with modern cyber threats. AI-powered detection helps identify suspicious activity, reduce false positives, and accelerate incident response
Traditional monitoring often misses subtle attack patterns and unusual user behavior, allowing threats to remain unnoticed until significant damage occurs.

Security teams receive thousands of alerts every day, making it difficult to identify genuine threats among false positives.
Fraudsters and attackers constantly adapt their techniques, making rule-based detection systems less effective over time.

Organizations struggle to correlate activity across applications, networks, cloud infrastructure, and user behavior, creating security blind spots.
Book A Call
Service
From a single AI-assisted feature to a full generative product layer, built to stay accurate to your data.
We build models that learn normal system and user behavior, then flag deviations that suggest a threat.

We apply machine learning to security logs to surface patterns manual review would miss.
We build detection systems for transaction fraud, account takeover, and platform abuse.
We continuously refine detection models to reduce false positives without missing real threats.
We continuously refine detection models to reduce false positives without missing real threats.

We optimize infrastructure choices to control inference and compute costs without sacrificing reliability.
Process
A structured approach to building, deploying, and optimizing AI-powered threat detection for faster and more accurate security monitoring.

Timeline: 1-2 weeks
We analyze historical activity and logs to establish what normal behavior looks like across your systems.
Deliverables:

Timeline: 3–6 weeks
We build and test anomaly detection models against historical incidents and known threat patterns.
Deliverables:

Timeline: Report & Remediate
We integrate detection into your monitoring stack and continuously tune it based on real alerts.
Deliverables:
Benefits
Identify unusual activity in real time with AI-powered monitoring that detects suspicious behavior much faster than manual log reviews, enabling quicker response to potential security incidents.

Reduce unnecessary security alerts through intelligent detection models that filter out noise, allowing your security team to focus on genuine threats.
Detect evolving fraud patterns, account takeovers, and malicious activities using machine learning that continuously adapts to new attack techniques.

Receive instant, actionable alerts that are routed to the right teams, helping your organization investigate and respond to threats without delay.
Build an AI-powered detection system that learns from real-world activity over time, improving detection accuracy and strengthening your overall security posture.
Use Cases

Protect patient-facing applications and healthcare systems with AI-powered threat detection that identifies unusual behavior, secures sensitive health data, and supports compliance with healthcare security standards.
 Apply AI-augmented threat detection to patient-facing platforms, care coordination tools, and clinical operations.Support compliance-aware builds for data-sensitive healthcare workflows.
Case Studies
Projects Of Novatore Solutions
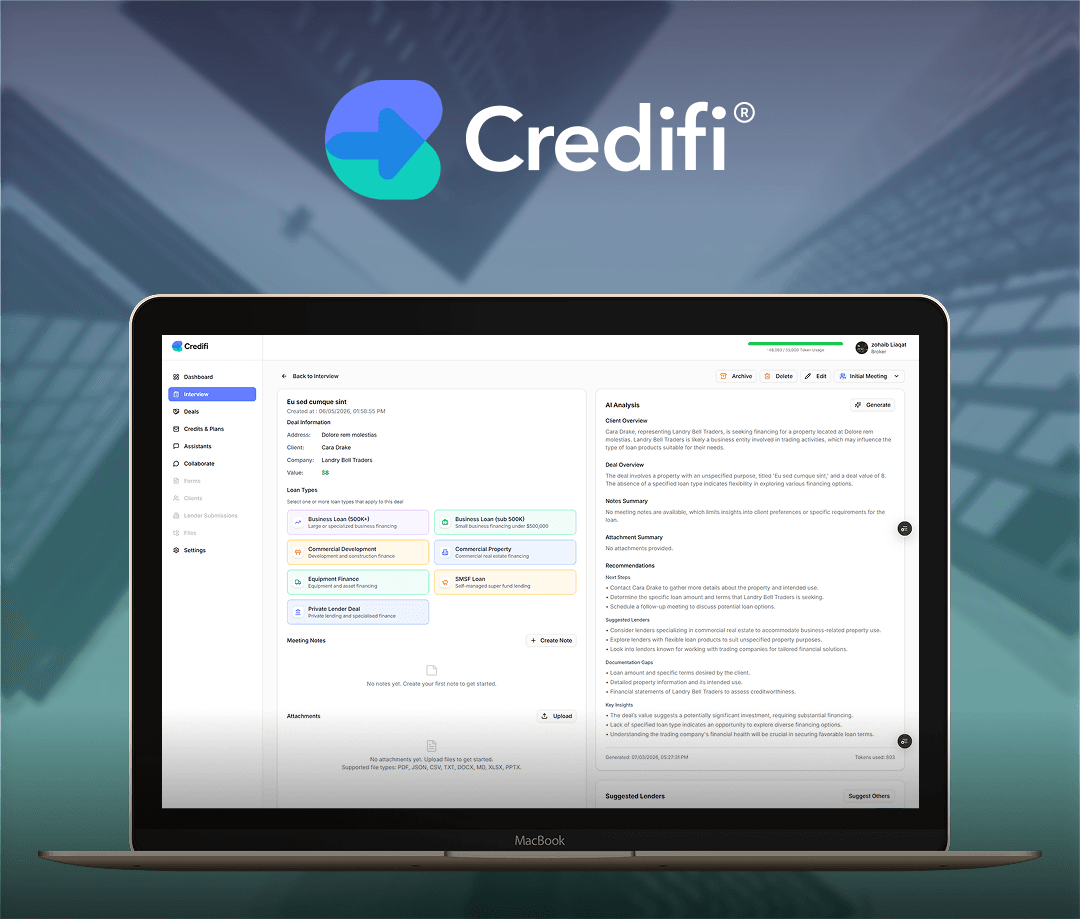
Kingdom Collective is a membership platform that manages user onboarding, group payments, and membership provisioning. AI-powered threat detection was implemented to monitor unusual user activity, secure payment workflows, and detect suspicious access patterns.
OUTCOME
Enhanced account security, reduced fraud risks, and strengthened customer trust.

Challenge: Detecting account takeovers, payment fraud, and abnormal user behavior without affecting the user experience.
Solution: We implemented AI-based anomaly detection, user behavior analytics, and real-time alerting integrated with the platform.
Result: Improved visibility into user activity, reduced false positives, and faster identification of suspicious events.
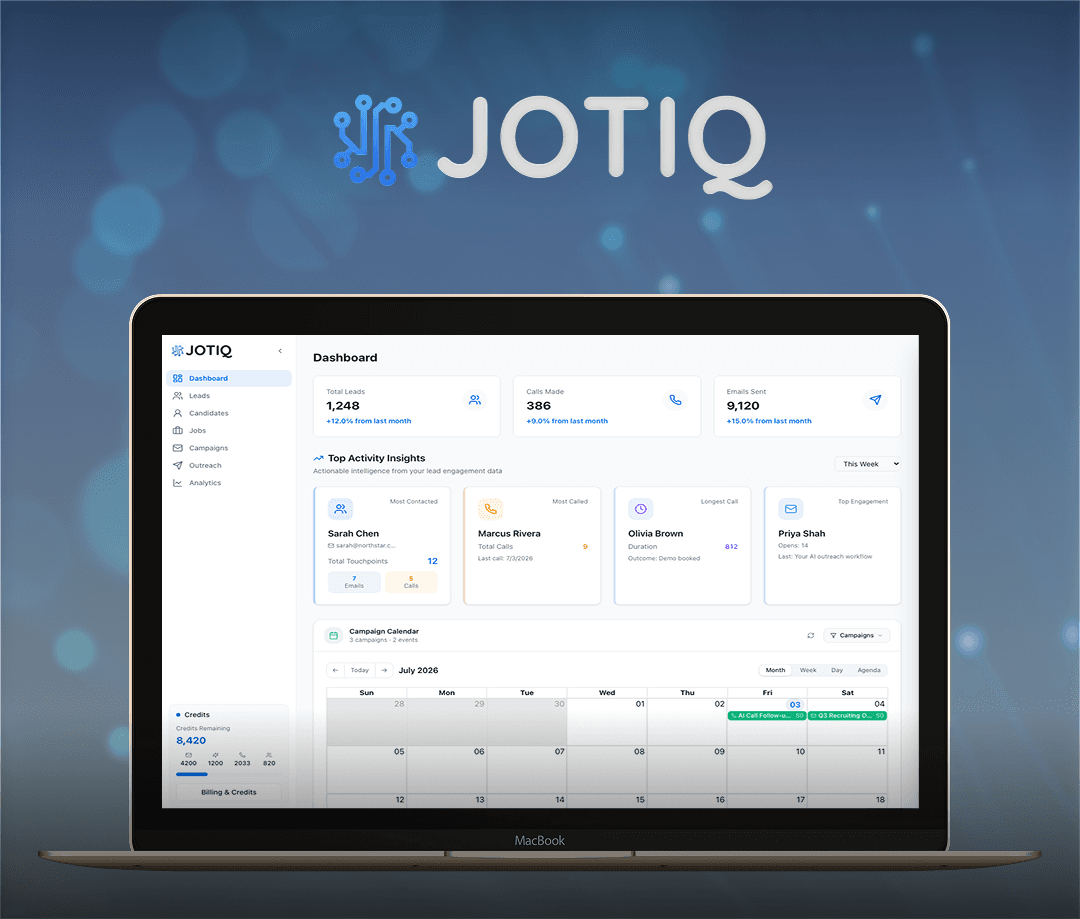
JOTIQ is an AI-powered recruitment and client outreach platform that automates hiring and sales workflows. Intelligent threat detection was designed to monitor unusual account activity, identify unauthorized access, and secure sensitive business data.
OUTCOME
Stronger platform security, better protection of customer data, and improved operational confidence.
Challenge: Protecting recruiter accounts, detecting suspicious login attempts, and monitoring abnormal platform usage.
Solution: We deployed AI-driven behavioral analytics, anomaly detection, and real-time security monitoring to identify potential threats.
Result: Improved threat visibility, faster incident detection, and more accurate security alerts.
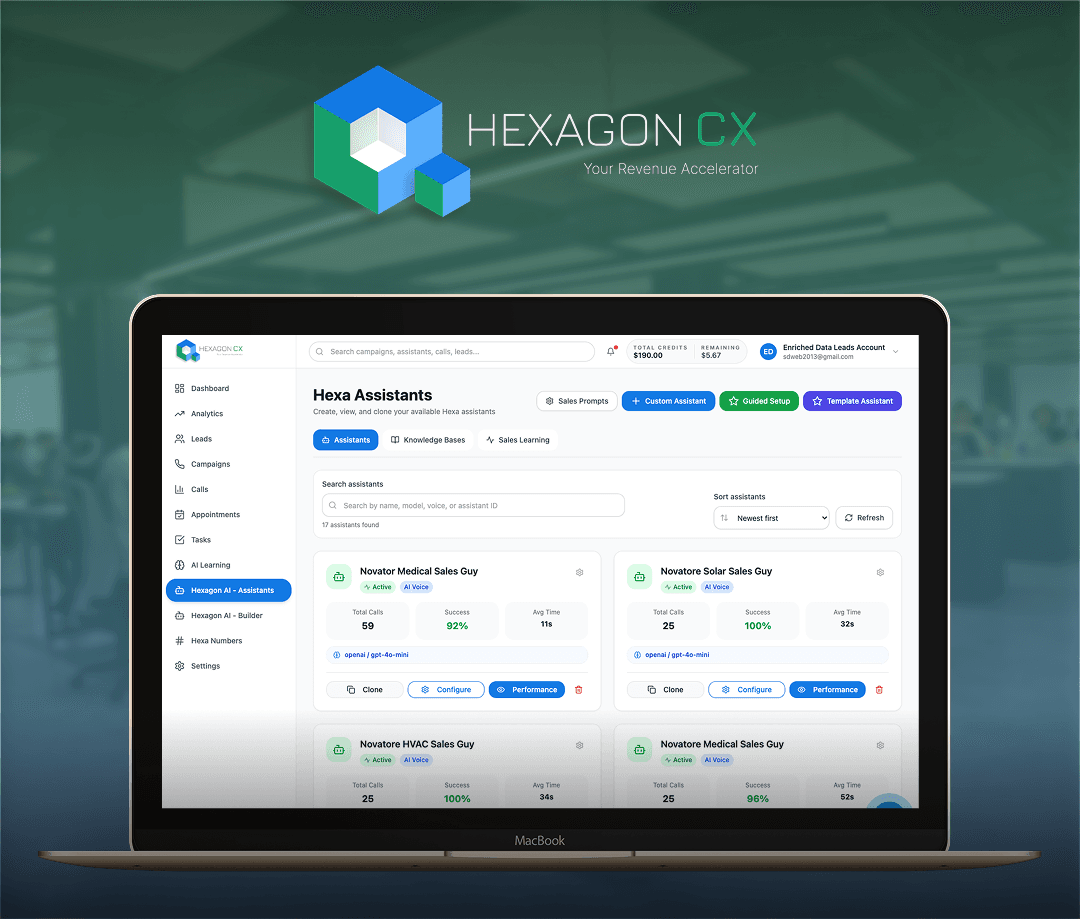
Gestion Hassani Inc. is a logistics platform that manages delivery requests, shipment tracking, invoices, and driver workflows. AI-powered threat detection was used to monitor operational activities, detect unusual access patterns, and secure critical business processes. Challenges
OUTCOME
Enhanced operational security, stronger data protection, and greater confidence in platform reliability.
Challenge: Detecting unauthorized access, monitoring unusual shipment activity, and protecting operational data across multiple user roles.
Solution: We implemented AI-based anomaly detection, user behavior monitoring, and real-time alerts to identify suspicious activities.
Result: Improved monitoring accuracy, earlier threat detection, and reduced false-positive alerts.
Tools & Technologies
Our strategy engagements are grounded in the same tools our delivery teams use, so roadmaps reflect what's actually achievable with today's AI platforms.


FAQ
What clients typically ask before building a generative AI feature into their product.
No, it augments it. We layer AI-driven detection on top of standard security monitoring, logging, and access controls, not in place of them.
More data improves accuracy, but we can start with a baseline detection setup even with limited history and refine it as more activity is observed.
We tune detection thresholds against real incident data and continue refining based on analyst feedback after deployment.
Yes, we typically integrate detection models with your existing SIEM or alerting tools rather than building a separate standalone system.
AI-driven monitoring can analyze activity continuously and generate alerts in near real time when behavior deviates from expected patterns, helping teams investigate potential threats before they escalate.
No. AI supports security teams by analyzing activity, identifying anomalies, and prioritizing alerts. Human experts remain responsible for investigating findings, validating threats, and deciding how to respond.
AI-powered detection can help identify unusual user behavior, account abuse, fraud patterns, suspicious network activity, insider threats, and automated bot activity across applications and infrastructure
Your Go To Business Partner
We combine strategy and delivery to build what actually ships, from roadmap to production

Strategists, engineers, and QA specialists work as one team to turn plans into software fast.

React, Next.js, Node.js, Flutter, and Laravel expertise, paired with modern AI and cloud tooling, covers the full delivery lifecycle.

We work inside the timelines, communication norms, and compliance expectations our North American and UK clients require.
38+ products delivered from concept to production across HealthTech, FinTech, retail, and SaaS, with proven experience
We are Just One Click Away
Book a discovery call with Novatore Solutions and let's map the right approach for your business.
CONTACT US
Have a challenge worth solving or an idea worth building? Let's explore it, shape it, and turn it into a solution that creates real impact.
