


Keeping Up With Changing Regulations
SOC 2, GDPR and ISO 27001 requirements keep changing. GRC consulting keeps you current.
Our GRC consulting services help you meet SOC 2, ISO 27001, HIPAA and GDPR requirements with practical controls, clear policies and an audit-ready evidence pack. We map your current gaps, fix them in priority order and prepare your team before the auditors arrive. Enterprise deals stop stalling on security reviews.
GRC Consulting Challenges
Governance, risk and compliance challenges that slow growth and stall enterprise deals.
SOC 2, GDPR and ISO 27001 requirements keep changing. GRC consulting keeps you current.

Many teams have good security practices but no written policies. Auditors need both.

Teams scramble to collect evidence before every audit. A compliance program keeps it ready.
Customers ask for SOC 2 reports and security questionnaires. Compliance readiness unblocks deals.
Book A Call
GRC Consulting Services
Compliance consulting services that turn frameworks into clear, achievable steps.
SOC 2 compliance consulting to get SOC 2 Type I and Type II ready with the right controls and evidence.

ISO 27001 consulting to build and certify an information security management system.
HIPAA compliance consulting to meet HIPAA privacy and security requirements for health data.
GDPR compliance consulting to handle personal data in line with GDPR and other privacy laws.

Cybersecurity risk assessment services to identify, rank and plan fixes for your biggest security risks.
AI governance consulting to set policies and controls for safe, compliant use of AI.
GRC Consulting Process
Our compliance process assesses your current posture, implements the missing controls and prepares you for a successful audit.

Timeline: 1-2 weeks
We assess your current security and compliance posture against SOC 2, ISO 27001, HIPAA or GDPR.
Deliverables: Compliance Gap Report Risk Register Framework Mapping Improvement Roadmap

Timeline: 2–3
We implement the missing controls, policies and documentation, in priority order.
Deliverables: Security Policies Standard Operating Procedures Implemented Controls Compliance Evidence Library

Timeline: 3–4 and ongoing
We organize evidence, validate controls and prepare your team for a successful audit.
Deliverables: Audit Readiness Checklist Evidence Package Compliance Documentation Security Questionnaire Responses
GRC Consulting Benefits
See exactly where you stand against SOC 2, ISO 27001, HIPAA or GDPR.
Security and operational risks identified and ranked.
Security policies and procedures written for your framework.
Your team and evidence prepared before the auditors arrive.

Technical and process controls implemented and documented.
GRC Consulting Use Cases
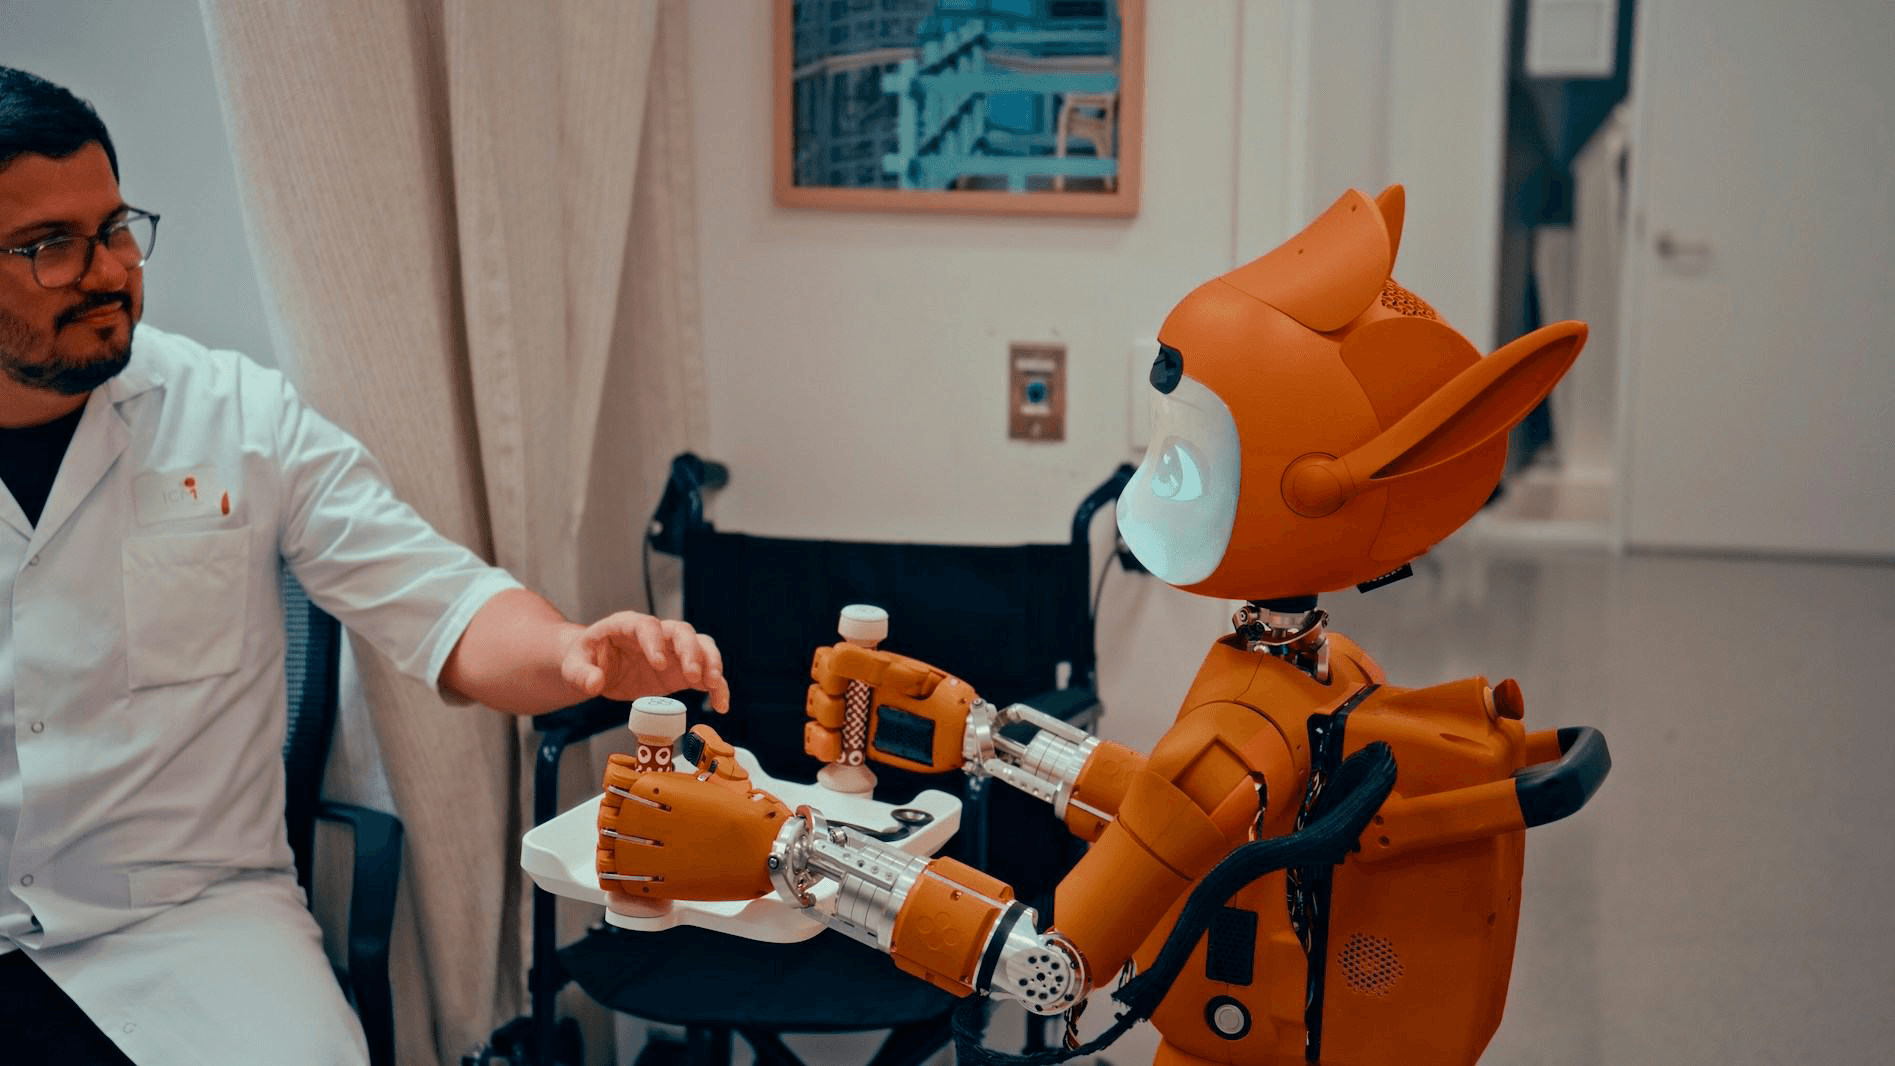

GRC for healthcare: HIPAA compliance programs for organizations that handle patient information.
 HIPAA compliance consulting for healthcare software.Risk assessments for systems holding patient data.Policies and controls for protected health information.Audit-ready evidence for HIPAA reviews.
GRC Consulting Case Studies
Selected Novatore projects related to grc consulting, with the challenge, the solution and the result.

Abimar Brokers is a WordPress-based platform supporting partnership and ownership structures within an internationally focused insurance brokerage. Novatore supported governance-aware practices appropriate for a regulated brokerage environment.
OUTCOME
Governance-aware data handling practices appropriate for a multi-jurisdiction, regulated brokerage environment.

Challenge: Abimar is an internationally focused insurance brokerage. It needed data handling practices that could stand up to regulatory scrutiny across multiple partnership and ownership structures.
Solution: Novatore applied a governance-aware approach to the platform's data practices, appropriate to the documented process and regulatory expectations of the insurance brokerage industry.
Result: The brokerage operates with data handling practices suited to an internationally regulated insurance context.
Read Case Study

A business insurance portal built on React, designed for startups and growth-stage companies to get insured and manage their insurance needs in one place. The platform centralizes insurance documents, contracts and renewals that would otherwise sit in email threads and paperwork. Growing businesses get one system to track their coverage.
Renewal Processing Time
40–50% faster
Challenge: The platform required stronger governance, secure document management, compliance documentation, and improved operational risk management.
Solution: We conducted compliance assessments, implemented governance controls, developed security policies, and established audit-ready documentation and ongoing compliance processes.
Result: The platform achieved improved governance, stronger security controls, organized compliance documentation, and streamlined compliance management.
Read Case StudyGRC Consulting Tech Stack
We use proven, production-grade tools and choose the right ones for each project based on performance, cost and security.


GRC Consulting FAQs
Answers to common questions about grc consulting services, including cost, timelines and how we work.
GRC is how a company sets its security policies, manages risk and proves it meets standards such as SOC 2, ISO 27001, HIPAA and GDPR. A GRC program maps your current gaps, fixes them in priority order and keeps the evidence that auditors and enterprise customers ask for.
It depends on your industry and customers; SOC 2 is common for B2B SaaS, while HIPAA and GDPR apply based on the data you handle. We help identify the right framework during the gap assessment.
Most businesses need two to four months to implement controls and documentation before a Type I audit, depending on current maturity.
No, formal audits are performed by accredited third-party auditors; we prepare your controls, documentation, and evidence so the audit goes smoothly.
No, many startups pursue SOC 2 or GDPR readiness early because enterprise customers require it before signing a contract.
Yes. We help organizations prepare for ISO 27001 by assessing existing controls, developing required policies, implementing security practices, and preparing documentation for certification readiness.
Most compliance frameworks require security policies, risk assessments, incident response plans, access control procedures, vendor management documentation, and evidence that controls are operating effectively. We help create and organize these documents.
Compliance is an ongoing process. We provide continuous support through periodic risk assessments, policy updates, control reviews, and audit preparation to help your organization maintain compliance as your business grows.
Novatore's rates are $25 to $49 per hour. Cost depends on your current controls, the framework and the audit scope. A gap assessment comes first and gives you a clear plan and estimate.
Why Novatore for GRC Consulting

We combine strategy and delivery to build what actually ships, from roadmap to production

Strategists, engineers, and QA specialists work as one team to turn plans into software fast.

React, Next.js, Node.js, Flutter, and Laravel expertise, paired with modern AI and cloud tooling, covers the full delivery lifecycle.

We work inside the timelines, communication norms, and compliance expectations our North American and UK clients require.
50+ products delivered from concept to production across HealthTech, FinTech, retail, and SaaS, with proven experience
Ready to know where AI actually pays off for you?
Book a free 30-minute discovery call. We'll review your goals, answer your grc consulting questions and suggest a clear next step, with no obligation.
CONTACT US
Have a challenge worth solving or an idea worth building? Let's explore it, shape it, and turn it into a solution that creates real impact.
